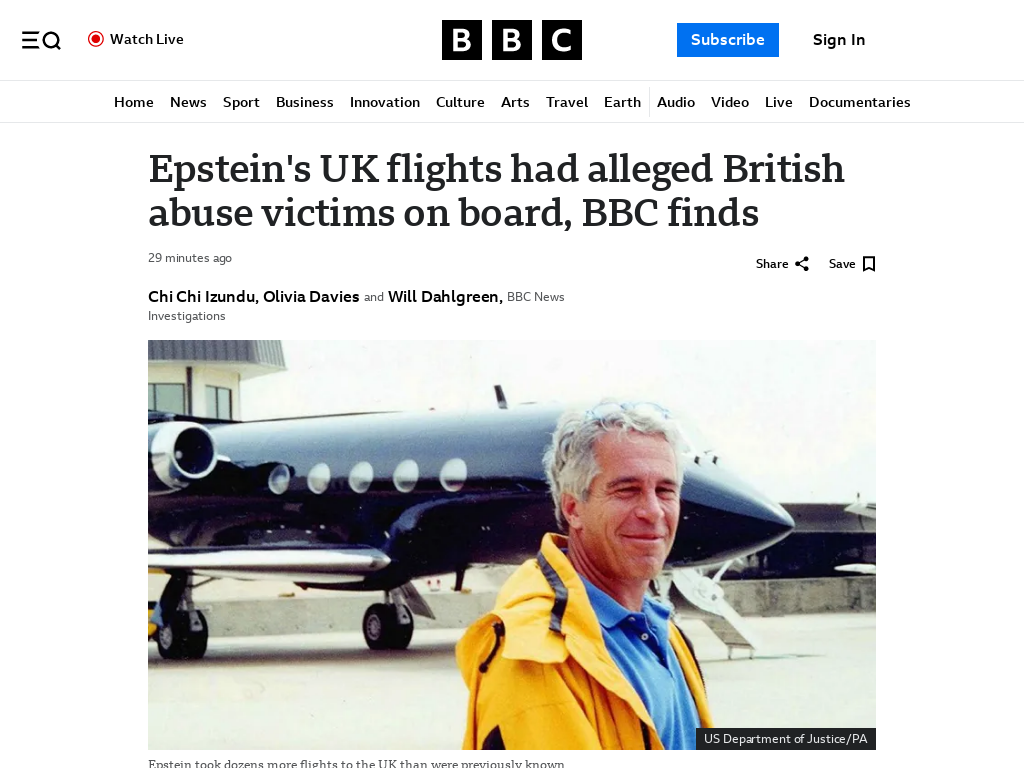
“Throwback: Reports of hackers accessing Jeffrey Epstein’s files” reports 100,000 of transactions through Carnivore or Magic Lanton that spy in certain situation on traffic on the internet.

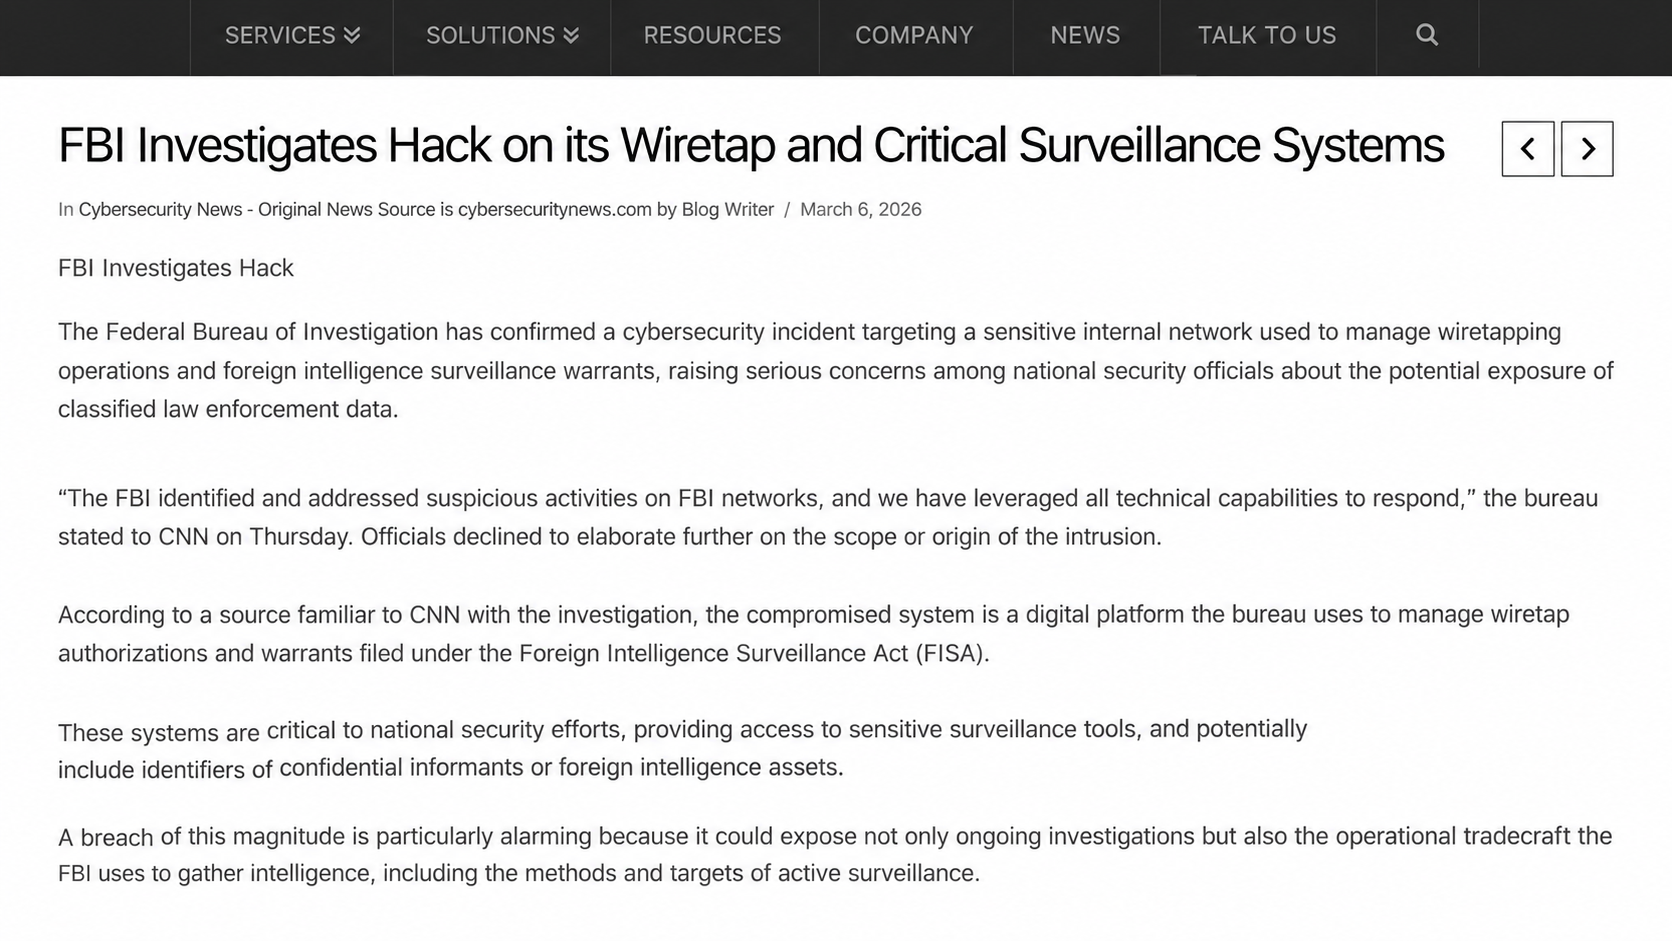
In the last couple of days, the FBI confirmed it had been the target of Hackers and that a cyber security event had occurred on its Wiretap and surveillance systems. This was reported on https://www.reuters.com/world/us/foreign-hacker-2023-compromised-epstein-files-held-by-fbi-source-documents-show-2026-03-11/
“FBI Investigates Hack on its Wiretap and Critical Surveillance Systems” — 6 March 2026.https://www.cryptika.com/fbi-investigates-hack-on-its-wiretap-and-critical-surveillance-systems/
The article says the FBI confirmed suspicious activity on an internal network used to manage wiretapping operations and foreign intelligence surveillance warrants. https://cybersecuritynews.com/fbi-investigates-hack/
I have independently checked this against CNN, CBS News and Associated Press reporting. KIFI+2
What was exposed to risk?
- Information connected with ongoing FBI investigations.
- Telephone numbers, internet identifiers and other surveillance-related data.
- Personally identifiable information about people under investigation.
- Sensitive information obtained through legal surveillance processes.
The FBI discovered abnormal system activity on 17 February 2026, according to its notification to Congress.
Now compare the two incidents
| Incident | Date | Systems involved |
|---|---|---|
| Epstein investigation files | February 2023 | FBI child exploitation forensic server |
| FBI surveillance network | February 2026 | Digital Collection System associated with wiretaps and surveillance orders |
Reuters separately reported the Epstein-related intrusion on 11 March 2026. Reuters
These are two documented security incidents involving particularly sensitive FBI systems. There is currently no established evidence that the same hackers were responsible or that the incidents were connected.
Who was to blame?
Alert Number: I-042425-2-PSA Date: April 24, 2025 Title: FBI Seeking Tips about PRC-Targeting of US Telecommunications seems to cast the shadow on “Salt Typhoon” who have been active since 2019.
It seems then there are now two places where you can obtain the Epstein files not just from the redacted FBI release of information covering up people who were allegedly involved alongside Epstein.

Now from a great write up at securityblvd.com they said that the actual information that was grabbed was not just intercepted communication as the warranted information was in something like “digital storm”. But what they actually got was DCS 300 or Redhook which held or allowed the access to warranted personal information in regard to people under investigation along with meta data to map communication patterns during criminal and national investigations.


Leave a Reply